Having a Backup Does Not Mean You Are Ready for a Disaster
Business continuity demands far more than routine backups; it requires a validated strategy for total operational resilience. Backups preserve data, but disaster recovery depends on your ability to restore systems and keep critical applications running during an outage. This relies on defining two key business metrics: Recovery Point Objective (RPO), which measures tolerable data loss, and Recovery Time Objective (RTO), which limits acceptable downtime. An untested plan is just an assumption. Resilience is measured not by documented procedures, but by proven recovery capabilities.
· 1 min read
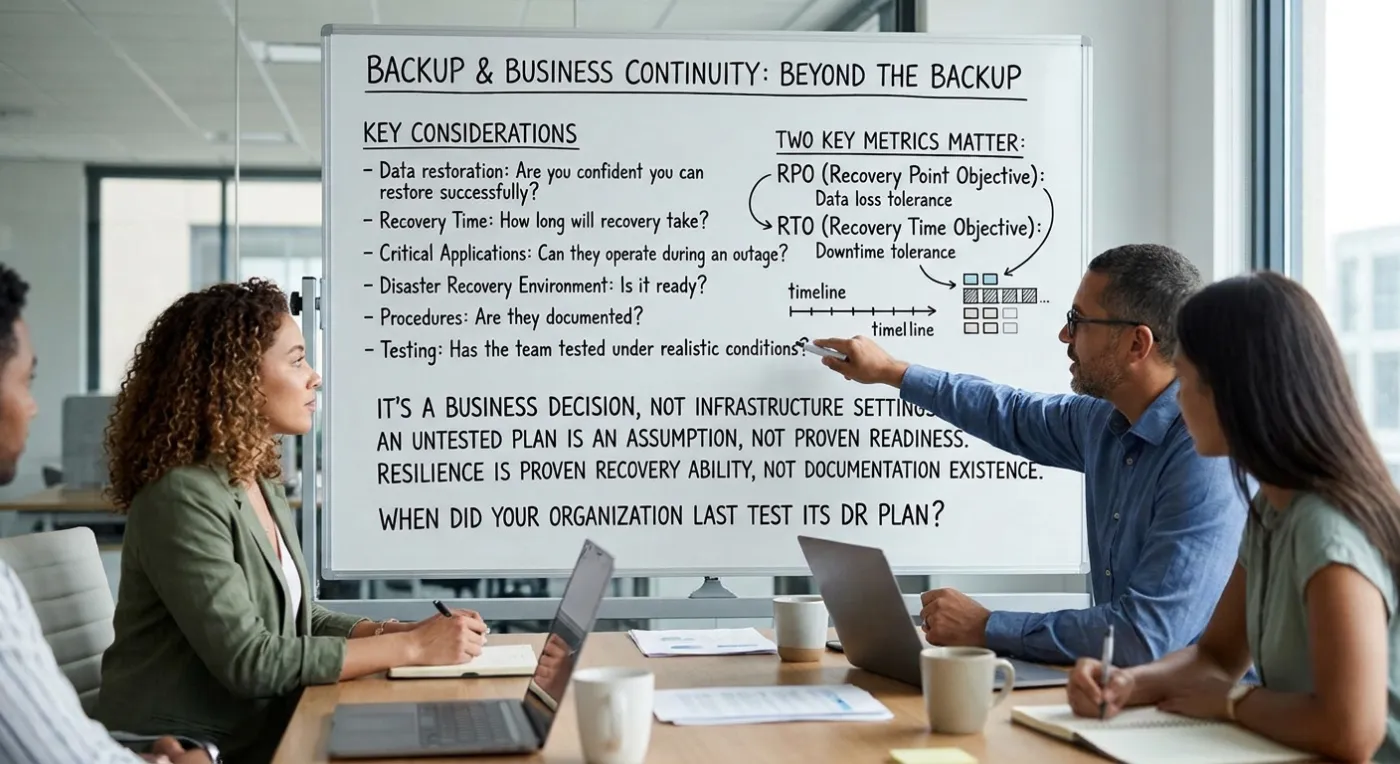
A backup is important, but it is only one part of business continuity.
Ask yourself:
• Can we restore the data successfully?
• How long will recovery take?
• Can critical applications operate during an outage?
• Is our disaster recovery environment ready?
• Are recovery procedures documented?
• Has the team tested the process under realistic conditions?
Two metrics matter here:
RPO — Recovery Point Objective: How much data loss can the business tolerate?
RTO — Recovery Time Objective: How long can the business tolerate being unavailable?
These are business decisions supported by technology, not just infrastructure settings.
A disaster recovery plan that has never been tested is an assumption, not proven readiness.
Resilience is not measured by the existence of a recovery plan. It is measured by the organization's ability to recover when it matters.
When did your organization last test its disaster recovery plan?
Share
Keep reading
Related articles
· 5 min read
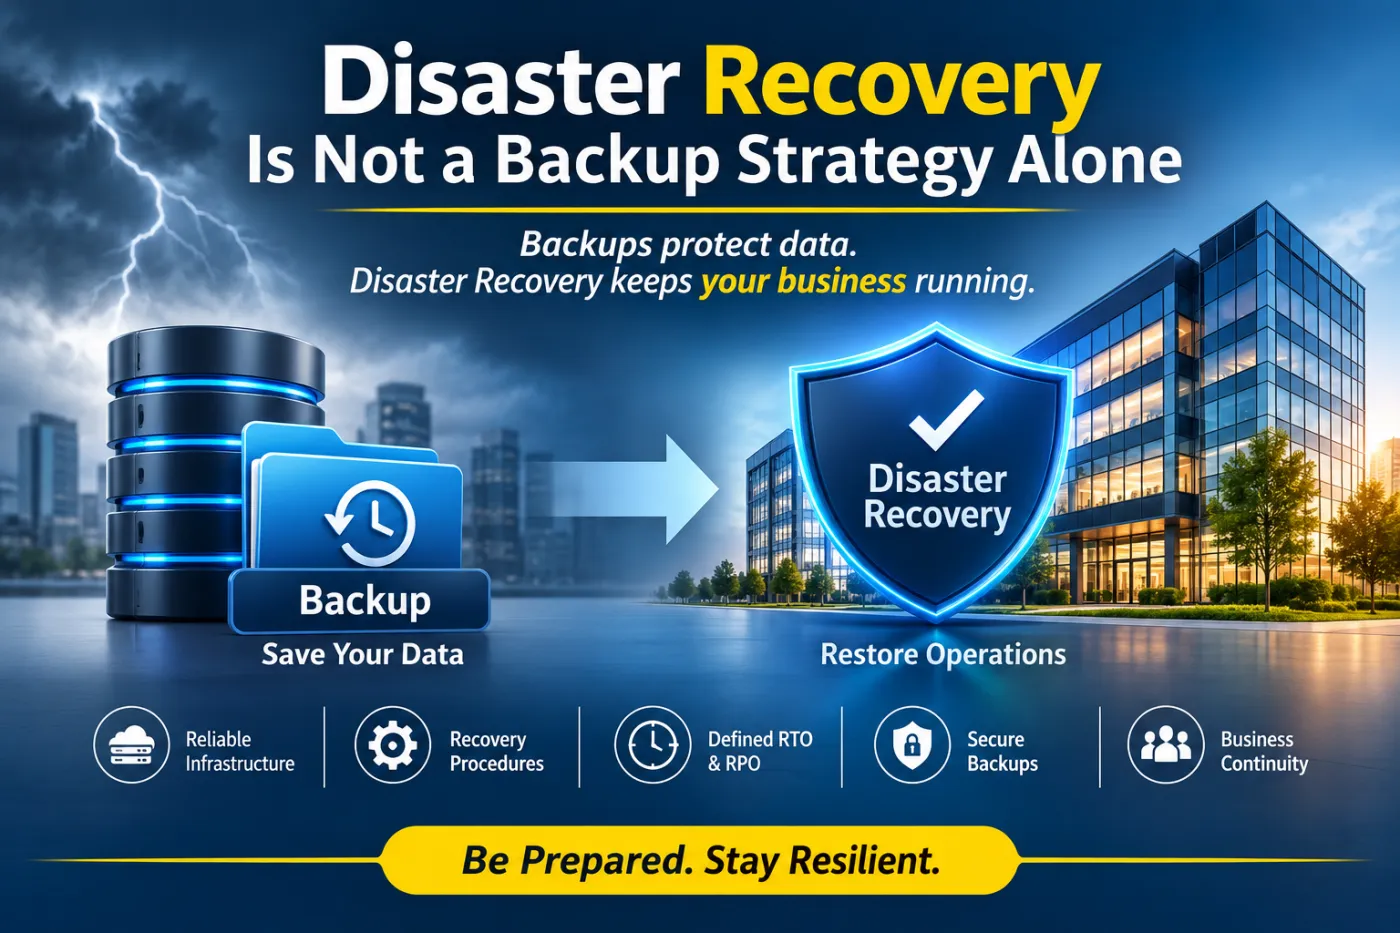
Disaster Recovery Is Not a Backup Strategy Alone
Disaster recovery is more than maintaining regular data backups. It is about ensuring that critical systems, applications, infrastructure, and business operations can be restored within acceptable timeframes when unexpected disruptions occur. A resilient organization prepares not just to protect its data, but to keep its business running.
Cybersecurity & Governance
· 2 min read
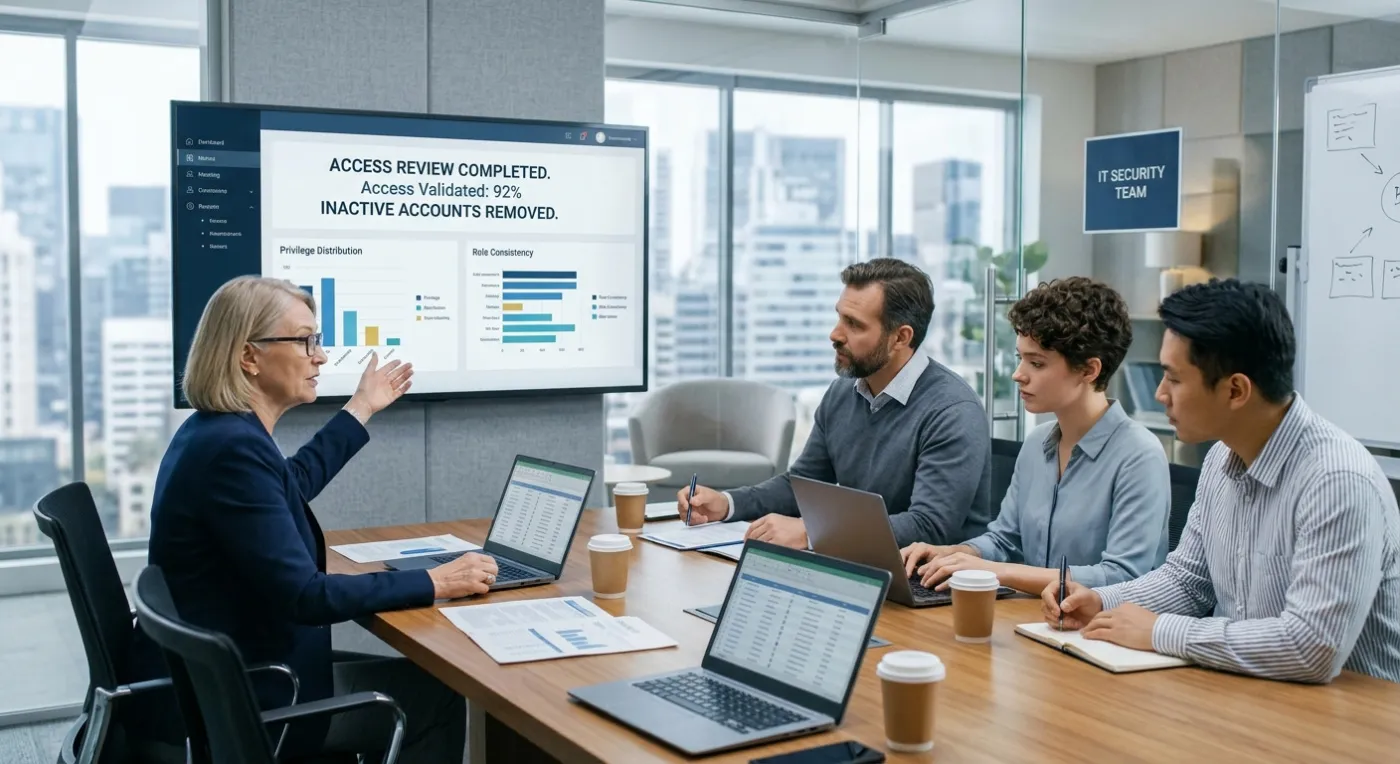
Why Access Reviews Matter More Than People Think?
Many organisations invest heavily in advanced cybersecurity tools, yet they frequently overlook one of the simplest security controls: regular access reviews. Over time, as employees shift roles and external contractors conclude their work, unmonitored privileges accumulate, leaving dormant or excessive permissions open. Technology and identity management systems alone cannot mitigate this risk; proactive governance is essential to constantly evaluate not just who holds access, but whether that access remains appropriate.
Cybersecurity & Governance
· 1 min read
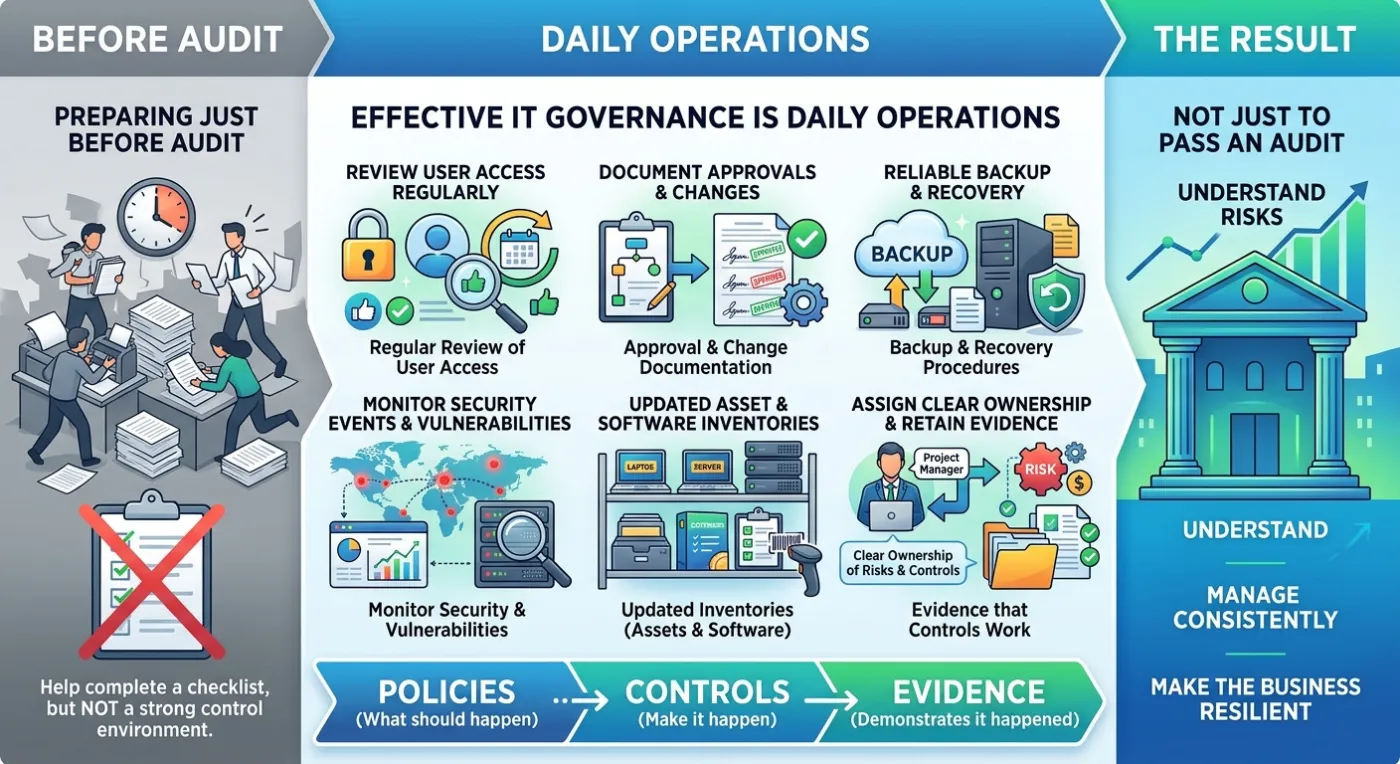
An Audit-Ready Organization Is Built Every Day, Not One Week Before the Audit
Effective IT governance is woven into the fabric of daily operations rather than assembled in a frantic scramble right before an audit. True control environments are built through consistent practices—such as regular user access reviews, meticulous approval documentation, reliable backup procedures, and clear risk ownership—transforming governance from a compliance checklist into an engine for operational resilience.
Cybersecurity & Governance