An Audit-Ready Organization Is Built Every Day, Not One Week Before the Audit
Effective IT governance is woven into the fabric of daily operations rather than assembled in a frantic scramble right before an audit. True control environments are built through consistent practices—such as regular user access reviews, meticulous approval documentation, reliable backup procedures, and clear risk ownership—transforming governance from a compliance checklist into an engine for operational resilience.
· 1 min read
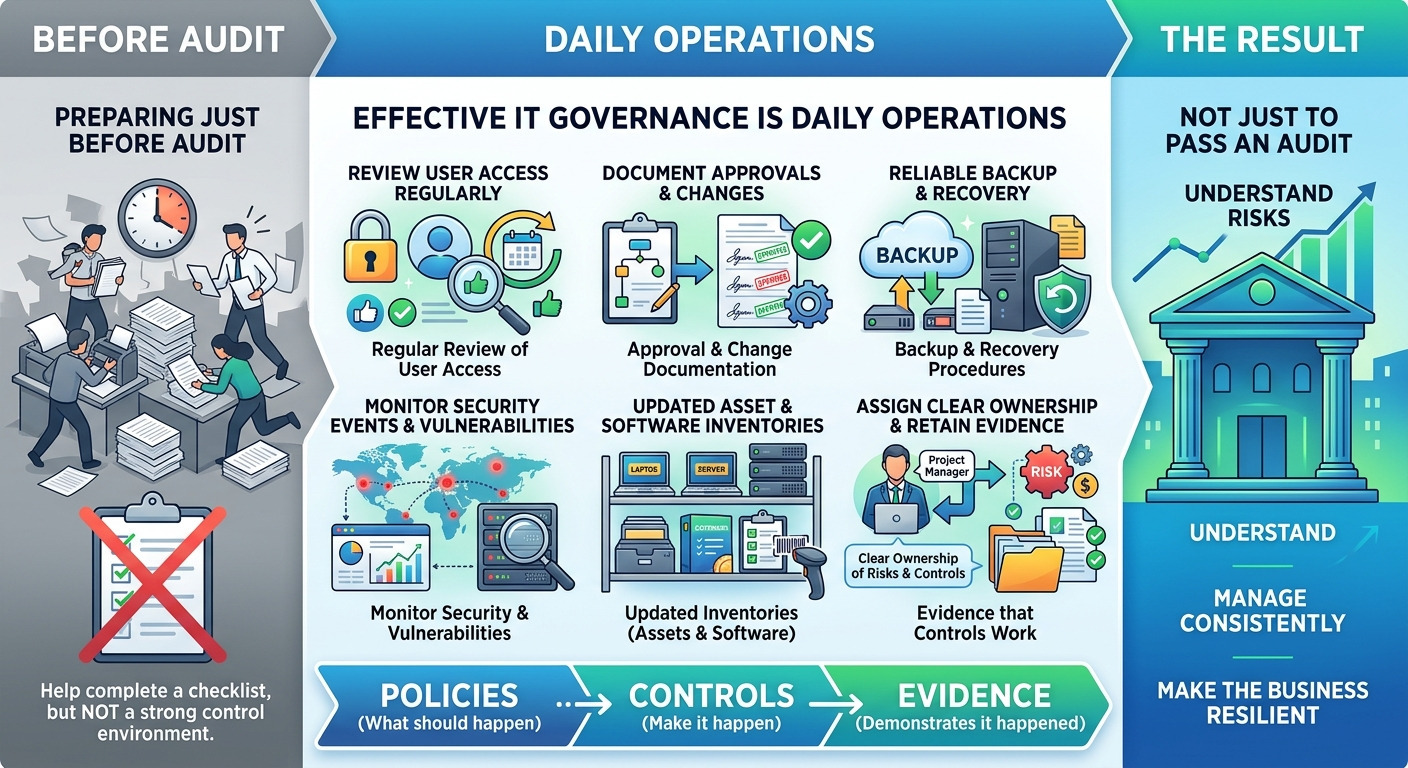
Preparing documents just before an audit may help complete a checklist, but it does not necessarily create a strong control environment.
Effective IT governance is part of daily operations.
It means:
• Reviewing user access regularly.
• Documenting approvals and changes.
• Maintaining reliable backup and recovery procedures.
• Monitoring security events and vulnerabilities.
• Keeping asset and software inventories updated.
• Assigning clear ownership to risks and controls.
• Retaining evidence that controls are actually working.
Policies describe what should happen.
Controls make it happen.
Evidence demonstrates that it happened.
The objective is not simply to pass an audit. It is to build an organization that understands its risks and manages them consistently.
Good governance should make the business more resilient, not merely produce more paperwork.
Share